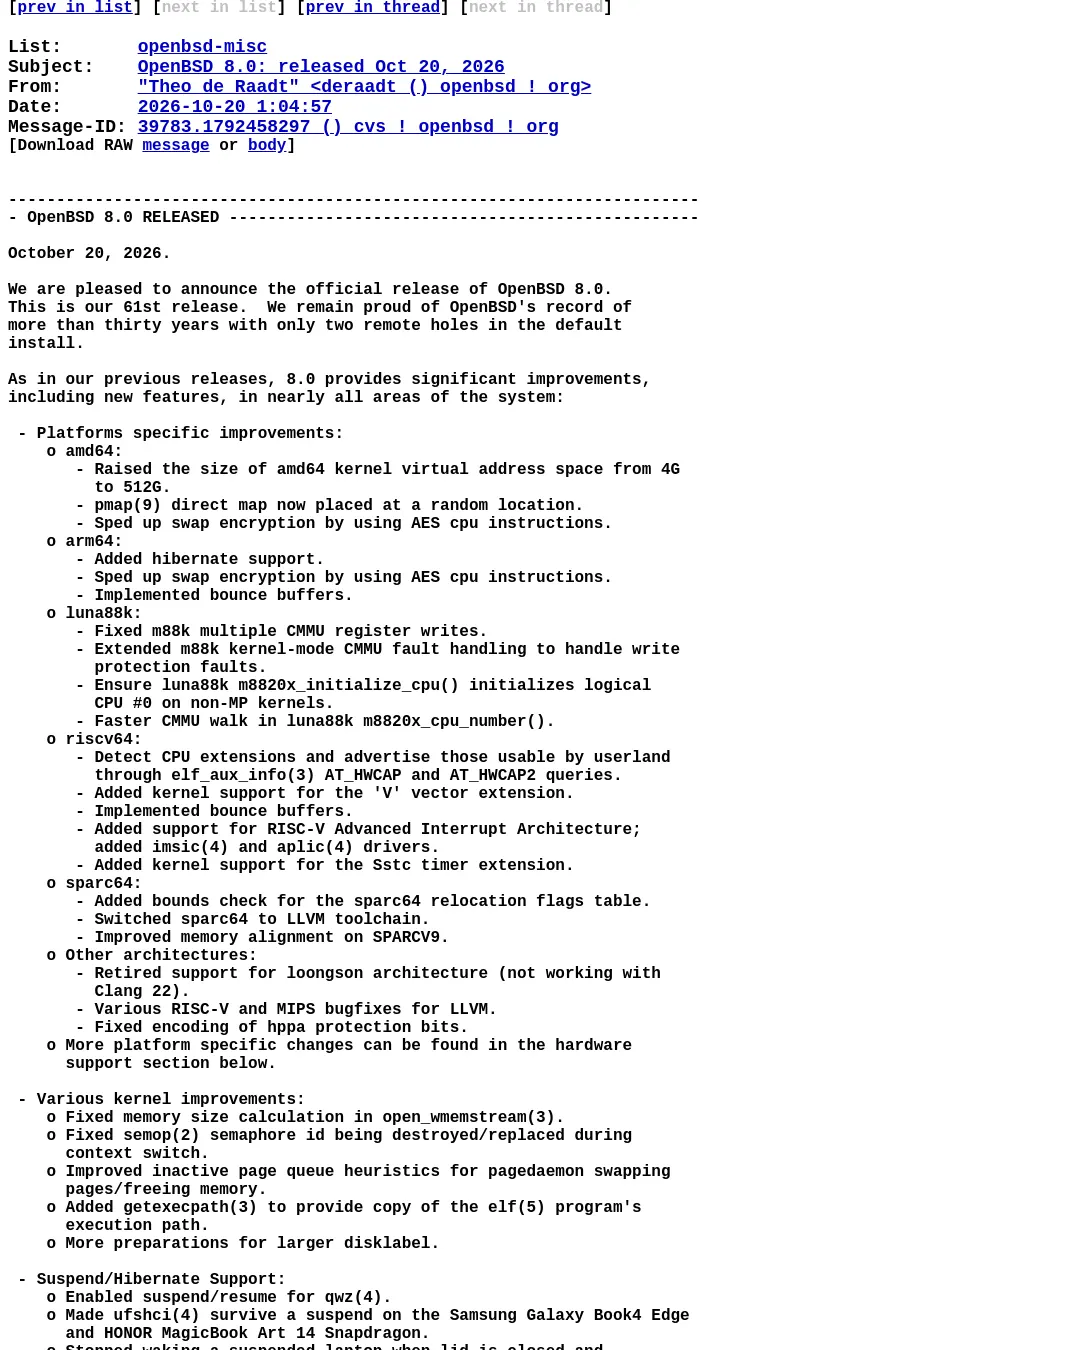
OpenBSD 8.0이 2026년 10월 20일 정식 출시됐다. 이번 61번째 릴리스는 보안 수정과 네트워크·가상화 개선, 여러 하드웨어 지원 확대를 포함한다.
amd64에서는 커널 가상 주소 공간이 4GB에서 512GB로 늘었고, Intel Arc A-Series 그래픽 카드 지원이 추가됐다. arm64에는 최대 절전 모드가 들어갔으며, RISC-V에는 벡터 확장과 인터럽트 아키텍처 지원이 추가됐다. 반면 Clang 22와 호환되지 않는 loongson 아키텍처 지원은 종료됐다.
가상 머신 관리 도구인 vmd(8)는 게스트당 최대 64개 가상 CPU를 지원하고, 32비트 Linux 게스트 지원과 체크섬 오프로드 기능 등이 개선됐다. 보안 측면에서는 OpenSSH 10.6과 LibreSSL 4.4.0을 포함하고, 시스템 전반의 취약점 수정과 입력 검증 강화가 이뤄졌다.
설치 파일은 OpenBSD 8.0 미러에서 받을 수 있다. 새 설치를 진행하는 경우 아키텍처에 맞는 설치 안내서와 이미지를 확인해야 하며, 릴리스 이후 수정 사항은 정오표에서 확인할 수 있다.
부록: 원문 예시
text
[prev in list] [next in list] [prev in thread] [next in thread]

List: openbsd-misc
Subject: OpenBSD 8.0: released Oct 20, 2026
From: "Theo de Raadt" <deraadt () openbsd ! org>
Date: 2026-10-20 1:04:57
Message-ID: 39783.1792458297 () cvs ! openbsd ! org
[Download RAW message or body]

------------------------------------------------------------------------
- OpenBSD 8.0 RELEASED -------------------------------------------------

October 20, 2026.

We are pleased to announce the official release of OpenBSD 8.0.
This is our 61st release. We remain proud of OpenBSD's record of
more than thirty years with only two remote holes in the default
install.

As in our previous releases, 8.0 provides significant improvements,
including new features, in nearly all areas of the system:

 - Platforms specific improvements:
 o amd64:
 - Raised the size of amd64 kernel virtual address space from 4G
 to 512G.
 - pmap(9) direct map now placed at a random location.
 - Sped up swap encryption by using AES cpu instructions.
 o arm64:
 - Added hibernate support.
 - Sped up swap encryption by using AES cpu instructions.
 - Implemented bounce buffers.
 o luna88k:
 - Fixed m88k multiple CMMU register writes.
 - Extended m88k kernel-mode CMMU fault handling to handle write
 protection faults.
 - Ensure luna88k m8820x_initialize_cpu() initializes logical
 CPU #0 on non-MP kernels.
 - Faster CMMU walk in luna88k m8820x_cpu_number().
 o riscv64:
 - Detect CPU extensions and advertise those usable by userland
 through elf_aux_info(3) AT_HWCAP and AT_HWCAP2 queries.
 - Added kernel support for the 'V' vector extension.
 - Implemented bounce buffers.
 - Added support for RISC-V Advanced Interrupt Architecture;
 added imsic(4) and aplic(4) drivers.
 - Added kernel support for the Sstc timer extension.
 o sparc64:
 - Added bounds check for the sparc64 relocation flags table.
 - Switched sparc64 to LLVM toolchain.
 - Improved memory alignment on SPARCV9.
 o Other architectures:
 - Retired support for loongson architecture (not working with
 Clang 22).
 - Various RISC-V and MIPS bugfixes for LLVM.
 - Fixed encoding of hppa protection bits.
 o More platform specific changes can be found in the hardware
 support section below.

 - Various kernel improvements:
 o Fixed memory size calculation in open_wmemstream(3).
 o Fixed semop(2) semaphore id being destroyed/replaced during
 context switch.
 o Improved inactive page queue heuristics for pagedaemon swapping
 pages/freeing memory.
 o Added getexecpath(3) to provide copy of the elf(5) program's
 execution path.
 o More preparations for larger disklabel.

 - Suspend/Hibernate Support:
 o Enabled suspend/resume for qwz(4).
 o Made ufshci(4) survive a suspend on the Samsung Galaxy Book4 Edge
 and HONOR MagicBook Art 14 Snapdragon.
 o Stopped waking a suspended laptop when lid is closed and
 machdep.lidaction=0.
 o Added a global sleep mode variable to distinguish hibernate from
 'normal' suspend.
 o Added suspend/resume support for qcuart(4).
 o Added support for wakeup interrupts to bytgpio(4), fixes IdeaPad
 resuming from suspend.
 o Validate size of chunks copied to piglet during hibernate
 unpacking of disk image.
 o Validate on-disk image sizes against integer overflow when reading
 chunks in unhibernate.
 o Prevent disk image overreads when reading the chunktable in
 unhibernate.
 o Clean up the framebuffer after unhibernate.
 o Made failure to allocate a dedicated queue for nvme(4) hibernate
 support non-fatal.

 - Direct Rendering Manager and graphics drivers:
 o Updated drm(4) to Linux 6.18.53.
 o Support for Intel Arc A-Series (DG2/Alchemist) graphics cards in
 inteldrm(4).
 o Increased kernel virtual address space on amd64 allows mapping
 more than 4GB of VRAM.
 o Workaround inteldrm(4) GuC timeout errors seen on some Alder Lake
 systems.

 - VMM/VMD improvements:
 o Added MP support for up to 64 VCPUs per guest VM.
 o Redesigned to use files to manage VM ownership.
 o Added x2apic mode support for guest virtual machines.
 o Fix for when vmd(8) does not detect kernel on startup.
 o Provide faulting GPA to vmd(8) for MMIO exits from vmm(4).
 o Refactored vmm(4) exit handling and correct RIP adjustment.
 o Added support for variable length instructions in VMX paths to
 vmm(4).
 o Prevent OOB reads by vmd(8) in 32 and 64-bit elf(5) loaders with
 malformed elf(5) files.
 o Implemented missing lapic/ioapic modes to fix vmd(8) support for
 32-bit linux guests.
 o Added checksum offload for vmd(8) guests.
 o MSI/MSI-X virtio device interrupt support added.
 o Support actually split split-virtqueues in vmd(8).
 o Added i82093aa ioapic and i82489dx-compatible lapic emulation to
 vmd(8).
 o Improved qcow handling.

 - Various new userland features:
 o netstat(1) can now print interface multicast counter; made '-q'
 more specific.
 o Adjusted ddb(4) default 'ps' output, print 'struct process' and
 'struct proc' separately.
 o Made mount(8) support DUIDs with -u; preserve DUID when updating
 file system.
 o Implemented control of midithru ports with sndioctl(1).
 o Allow list elements to be added or removed by sndioctl(1).
 o Added the sndiod(8) server.mode control making the setting
 dynamic, changeable via sndioctl(1).

 - More bugfixes and tweaks in userland:
 o Ensure elf(5) header and program header fit into the shared
 library when loading.
 o Fixed leak of key memory in getpwent(3) yp_next().
 o In patch(1), solved an infinite loop on malformed ed(1) script
 input.
 o Use execv(3) absolute-path in authpf(8), pflogd(8), ldapd(8),
 ldpd(8), lpd(8), radiusd(8), snmpd(8).
 o uaudio(4) now tests the reported format and channels are usable.
 o Stopped sndiod(8) aborting if a MIDI endpoint connects with
 non-empty buffers.
 o Fixed two missing checks of file_new() return value in sndiod(8).
 o Fixed npppd(8) LCP MRU option handing.
 o Adjust pstat(8) to return the pid of the session leader process;
 allow '-t -M' to work.
 o Made eigrpd(8) validate the prefixlen to avoid overflow.
 o Made sndiod(8) allocate all midithru structures on the heap.

 - Improved hardware support and driver bugfixes, including:
 o Enabled the GXTP7936 touchscreen on the Samsung Galaxy Book4 Edge.
 o Added support for the riscv64 K3 PCIe/USB3 combo PHY.
 o Enabled gpioleds(4) on riscv64.
 o In smte(4) (SpacemiT K1 Ethernet device), improved error checking
 of received packets.
 o Fixed regular MSI interrupts on the SpacemiT K1 SoC.
 o Added support for the SpacemiT K3 SoC to smtclock(4).
 o Added SC7280 support to qcgpio(4).
 o Added support for the SpacemiT K3 dwpcie(4) PCIe controller.
 o Added RK3528 I2C5 clock, used in the Radxa E24C.
 o Added ACPI hardware IDS for Qualcomm Glymur (X2) SoC.
 o Implemented page table mirroring in apldart(4); enable IOMMU for
 Apple USB controllers.
 o New samsabi(4) driver for the Samsung Advanced BIOS Interface
 (SABI).
 o New sambat(4) driver for Samsung laptop battery monitor.
 o New rkotp(4) driver for Rockchip OTP memory.
 o Added support for the RK8600 regulator used for CPU voltage on
 Radxa Zero 3 boards.
 o Added more AMD "Krackan Point" device ids.
 o Fixed HONOR MagicBook Touchpad multitouch support.
 o Fixed esp(4) FIFO memory overflow.
 o Fixed potential memory leak in softraid(4) rebuild.
 o Fixed softraid(4) rebuild on disks with 4096-byte sectors.
 o Fixed high memory mbufs for 64-bit DMA capable re(4).

 - New or improved network hardware support:
 o Added support for Panther Lake and Wildcat Lake Ethernet devices
 to em(4).
 o Added support for Intel E610 Ethernet devices to the ix(4) driver.

 - Added or improved wireless network drivers:
 o Properly handle potential case of empty packets returned from
 qwx(4) hardware.
 o Added missing DMA syncs for qwx(4) SRNG DMA descriptor memory.
 o Properly handle qwx(4) VIF DMA map allocation failures at attach
 time.
 o Fixed use of stale pointers on the qwx(4) vif list which caused
 crashes.
 o Properly reset qwx(4) driver and device state if it fails to get
 RUNNING in qwx_init().
 o Avoid race condition in qwx(4) device during power-on.
 o Use the ioctl rwlock correctly in qwx(4) qwx_activate().
 o Ensure qwx(4) rx_ring->bufs_max and freemap are always initialised
 correctly.
 o Stopped qwx(4) init task waiting for the ioctl lock to become
 available.
 o Made qwx(4) properly errors which occur in qwx_qmi_fw_init_done().
 o Fixed roaming between APs with qwx(4).
 o Always allow data frame interrupts in qwx(4) while the interface
 is UP.
 o Added support for 40MHz channels to qwx(4).
 o Made qwx(4) only allocate a new mbuf when a free Rx ring slot is
 available.
 o Avoid calling bus_dmamap_create() from interrupt context in
 qwx(4).
 o Handle country code events sent by qwx(4) firmware to make
 association more reliable.
 o Reset qwx(4) command ring 'queued' counter when the command ring
 gets reset.
 o Ensure that qwx(4) nq flags are always cleared when switching
 net80211 state.
 o Fixed number of tx/rx streams set in qwx(4) mac config.
 o Made qwx(4) send the PMF good-bye deauth frame when hopping out of
 RUN state.
 o Ensure no new tasks get scheduled while IFF_RUNNING is in
 qwx_stop(). Prevents qwz(4) crash.
 o Make qwx(4) prefer ic_bss over the ephemeral node in the scan
 tree.
 o Add peer to qwx(4) firmware after starting the vdev, not before.
 Fixes a firmware crash.
 o Add 802.11n support to qwx(4). Advertise HT capabilities and pass
 HT/QoS peer association.
 o Ask qwx(4) firmware to move into M3 state before resetting the
 device.
 o Avoid calling bus_dmamap_destroy() from interrupt context in
 qwx(4).
 o Added 802.11n with 40MHz width to qwz(4).
 o Let qwz(4) handle QoS in native WiFi frames.

 - Installer, upgrade, bootloader, and pkg-tools improvements:
 o Harmonise installurl(5) handling in pkg_add(1), sysupgrade(8), and
 syspatch(8).
 o Fixed free space check by fw_update(8) for unqualified filenames.
 o Set limit on the size of files fw_update(8) can download.
 o Stricter validation in fw_update(8) to no longer treat untrusted
 comments as data.
 o pkg_add(1) now detects and overcomes some endless loops with
 merge-sets.
 o Clean trailing slashes from fw_update(8) FWURL.
 o Removed current directory from default pkg_add(1) search path.
 o Improved downloading of firmware by filename in fw_update(8).
 o Improved fw_update(8) error when SHA256.sig is not found.
 o fw_update(8) now checks signature of local SHA256.sig.
 o In fw_update(8), made tar(1) skip files outside expected
 locations.
 o Stopped syspatch(8) downloading entire tgz file when looking for a
 potential update.

 - Security improvements:
 o Fixed a pledge(2) in vfs(9).
 o Fixed out-of-bounds access attempts on aplmca(4) SOCs.
 o Stopped use of non-standard UID_MAX and GID_MAX in various
 utilities.
 o Improved ipsec(4) AES GMAC crypto.
 o Made iked(8) reject malformed and out-of-state IKEv2 messages.
 o Plugged memleak in x509_verify (CID 656293).
 o Avoid overflow in sysctl(2) KERN_PROC_ARGS.
 o Prevent bogus or malicious iaddr data from crashing dhcpd(8).
 o Avoid potential memory exhaustion via DHCPINFORM in dhcpd(8).
 o Properly use saltlen and min_saltlen in libcrypto RSA-PSS.
 o Reject invalid delta CRLs in libcrypto x509.
 o Fixed RFC 3779 inheritance handling in libcrypto's path
 validation.
 o Use execve(2) as $ORIGIN in ld.so(1) (otherwise fallback to
 realpath).
 o Hardened syspatch(8) against malicious scripts.
 o Restrict the characters that are allowed to pass through smtpd(8)
 environment and mda.
 o Fixed reading past the NUL by pax(1).
 o Stopped pax(1) extracting malicious archives outside the working
 directory.
 o Added 'mcast' to the pledge(2) for lldpd(8).
 o Tightened pledge_sockopt() level/optname checks for different
 types of sockets.
 o Extended the 'mcast' pledge(2) to allow multicast tweaks on
 Ethernet frame sockets.
 o Updated libexpat to version 2.8.4 (CVE-2026-66046 CVE-2026-76641
 CVE-2026-76957).
 o Avoid script pathname TOCTOU in exec when the vnode changes.
 o Made execve(2) realpath processing more robust.
 o Switched luna88k to build kernel files with -fno-pie.
 o Unprivileged kernel memory read and write vulnerability removed
 from m88k 88100 data pipeline.
 o unveil(2) now restricts man(1), makewhatis(8), and man.cgi(8) read
 and write access.
 o dhcpleased(8) now validates the IP address the dhcp server acks.
 o Fixed signed integer overflow in perl(1) Storable
 (CVE-2026-57433).
 o Fixed integer overflow in perl(1) pack and unpack
 (CVE-2026-57432).
 o Fixed perl(1) incorrect regular expression matches
 (CVE-2026-13221).
 o Fixed memory leaks and race condition in profil(2).
 o Improved checking of elf(3) notes; prevent out of bounds access.
 o Reject elf(3) interpreters without loadable segments.
 o Disable kbind(2) and pinsyscalls(2) for static binaries inside
 exec_elf_makecmds().
 o Fixed elf(5) structs to avoid leaking kernel stack contents.
 o LibXfont 2 fixes for CVE-2026-56001, CVE-2026-56002, and
 CVE-2026-56003.
 o Xserver(1) fixes for CVE-2026-55999 and CVE-2026-56000.
 o Updated perl(1) Socket to 2.041 (contains fix for CVE-2026-12087,
 out-of-bounds heap read).
 o Fixed iked(8) to bzero(3) the mask data structure, rather than
 using mask4.
 o Fixes for CVE-2026-12244, CVE-2026-12245, CVE-2026-12246 and
 CVE-2026-12490 in nsd(8).
 o Stopped leaking transport in isakmpd(8) error paths of
 udp_encap_handle_message().
 o Enforce per-type ID payload size in isakmpd(8)
 ipsec_validate_id_information().
 o Avoid shift overflows in memmem(3) and strstr(3).
 o Multiple additional bounds checks in isakmpd(8).
 o Provide a separate executable file for syslogd(8) parent, for
 privilege separation.
 o Made smtpd(8) clear userinfo before sending over imsg.
 o Made smtpd(8) reject oversized sockaddr payloads received over
 privsep IPC.
 o Zero the temporary smtpd(8) envelope parsing buffers before use to
 strengthen privsep.
 o Clear pending asynchronous lookups at teardown, for stronger
 smtpd(8) privsep.
 o Fixed potential information leak from an uninitialised ktrace(1)
 stack variable.

 - New features in the network stack:
 o Set ice(4) link state to full duplex.
 o Reduced maximum TSO segs in ice(4), to allow more interfaces to
 attach.
 o Enabled use of 128 DMA segments for TSO packets on ice(4).
 o Enabled 64-bit DMA for bge(4) BCM5720.
 o Enabled jumbo frames in ogx(4).

 - Further changes and bugfixes in the network stack:
 o Stopped ipsec(4) overflowing the maximum packet size in the IP
 header.
 o Detect out of bound reads from an int overflow in the bpf(4)
 bpf_mem backends.
 o Moved bpf(4) for outgoing packets later in the transmit path.
 o Avoid leaking memory when mbuf chain allocations fail in tun(4)
 tun_dev_write().
 o Fixed hardmtu and rxmax in ixl(4).
 o Handle dynamic channel width changes correctly in iwx(4).
 o Hardened bpf(4) bpf_filter; block unhandled instructions with
 bpf_validate.
 o Added proper program bound checks to the bpf(4) engine (libpcap
 CVE-2026-31912).
 o Fixed bpf filter calls in ppp(4); use bpf_mfilter(9).
 o Improved imsg handling of LS_UPD, LS_FLOOD and LS_SNAP in
 ospfd(8).
 o Changed ospfd(8) imsg handling.
 o ospfd(8) now adds missing rtlabel references and update routes
 when only the label changes.
 o Preserve configured interface type on ospf6d(8) link update.
 o Ensure ospfd(8) does not leak information on memory address layout
 from process.
 o Made authpf(8) read_config() remove trailing white space to avoid
 misconfigurations.
 o Fixed veb(4) SIOCBRDGRTS and SIOCBRDGVRTS ioctls leaking kernel
 stack data.
 o Fixed packet corruption in veb(4).
 o veb(4) now returns ENOMEM when mallocarray() fails in
 veb_rule_list_get().
 o Fixed ifconfig(8) 'vebX -tagged ifX' which accepted too many
 arguments.
 o Improved em(4) K1 exit timeout, to receive non-broadcast packets.
 o Simplified mac type tests on em(4).

 - The following changes were made to the pf(4) firewall:
 o Fixed off-by-one in pf(4) ioctl DIOCIGETIFACES.
 o Do not free the pf(4) caller's ruleset when attaching a table
 fails.
 o No longer allow un-terminated strings in pf(4) ioctl's.
 o Stopped pf(4) dropping valid MLD packets with unspecified source
 address.
 o Prevent pf(4) dropping TCP state if it receives a crafted reset
 packet.
 o Fixed races in pf(4) connection counters that caused connection
 counter underflows.
 o Fragment reassembly in pf(4)/inet(4)/inet6(4) now occurs in
 correct routing domain.
 o Stopped 'pfctl -s all' dumping all OS fingerprints loaded to
 pf(4).
 o Fixed NULL pointer dereference in pf(4) outbound packet path.
 o Fixed out-of-bounds read in pf(4) pf_rule_copyin().

 - Routing daemons and other userland network programs saw the following
 improvements:
 o Altered smtpd(8) code to avoid false bug reports from LLM
 scanners.
 o Prevent size_t underflow on a malformed packets in agentx(3) and
 snmpd(8).
 o Widen httpd(8) server flags to 64-bit integers.
 o httpd(8) now enforces 'max request body' for chunked requests
 passed to fastcgi.
 o Made httpd(8) reject config of shared TLS listeners with different
 client CA or CRL.
 o In httpd(8) now sends one imsg fastcgi param struct per parameter,
 to preserve config order.
 o Added custom HTTP header support to httpd(8).
 o Fixed httpd(8) suffix range handling.
 o Stopped httpd(8) sending location fcgiparams twice.
 o Made httpd(8) drain abort response via bufferevent to prevent
 errors being truncated.
 o Restricted IMSG_CTL_PROCFD to parent and check process id/instance
 in iked(8), httpd(8), relayd(8), and snmpd(8).
 o Switched the default TLS cipher in httpd.conf(5) set from 'compat'
 to 'secure.'
 o Made httpd(8) and dhcpd(8) correctly error check timegm(3).
 o Random-relink smtpd(8) and httpd(8) at boot.
 o httpd(8) now rejects CL.TE request framing (per RFC 9112 sections
 6.1 and 6.3).
 o Made httpd(8) reject obs-fold with 400 (RFC 9112 5.2).
 o Fixed uploads using httpd(8) chunked transfer-encoding.
 o httpd(8) will now advertise Vary: Accept-Encoding whenever
 gzip-static is enabled.
 o Made httpd(8) advertise static file revalidation, preserving
 Last-Modified and If-Modified-Since flow.
 o Added more config checks to relayd(8).
 o Explicitly flush relayd(8) redirect rules after reloading.
 o In relayd(8), removed wrong disable flag for routers.
 o Use a per-host random ICMP echo id in relayd(8).
 o Added Lua patterns(7) support for relayd(8) filter rules; improved
 glob(7) documentation.
 o Use getexecpath(3) and execv(3) in bgpd(8) eigrpd(8), httpd(8),
 iked(8), ntpd(8), relayd(8), and smtpd(8).
 o Fixed relayd(8) deferring connections log.
 o Made relayd(8) check proc_compose and imsg_compose_event return
 values.
 o Allow setting log level from relayd.conf(5).
 o Added ECDSA support to the relayd(8) CA privsep engine.
 o relayd(8) now rejects duplicate Content-Length headers with 400.
 o Switched the default TLS cipher in relayd.conf(5) set from
 'HIGH:!aNULL' to 'secure.'
 o Switched relayd(8) to new imsg API.
 o Made relayd(8) strip Content-Length for chunked messages (RFC 9112
 section 6.1).
 o Made relayd(8) reject obs-fold to prevent parser differentials
 (RFC 9112 5.2).
 o Removed relayd(8) X509_dup() call that leaks memory; add error
 checks for X509_set_*.
 o In relayd(8), added support for the MKCALENDAR HTTP method.
 o Fixed debug build of relayd(8).
 o Let relayd(8) support multiple resolvable addresses.
 o Let relayd(8) handle HTTP responses without bodies.
 o Fixed NULL dereference in isakmpd(8) message_alloc_reply()
 callers.
 o Fixed possible unaligned 32-bit read by isakmpd(8).
 o Validate isakmpd(8) DELETE payload SPI array size.
 o Validate proposal and transform sizes in isakmpd(8).
 o Added length checks for the Port-Message and State attributes in
 login_radius(8) Access-Challenge.
 o Prevent the dhcpleased(8) engine from sending us a negative amount
 of routes.
 o Made dhcpleased(8) accept correct amount of routes from the engine
 process.
 o Make sure dhcpleased(8) UDP header length field at least covers
 the UDP header.
 o Extended smtpd(8) mask-src to suppress session details.
 o Switched smtpd(8) over to imsgbuf_get(3).
 o Free dispatcher in smtpd(8) mda_envelope_free() to avoid a leak.
 o smtpd(8) now rejects empty or slash-bearing usernames before
 building the mbox path.
 o smtpd(8) now rejects CR/LF in argv-derived fields before starting
 the SMTP enqueue dialogue.
 o Properly free the copied envelope on the smtpd(8) smarthost lookup
 failure path.
 o Properly free mda_subaddress in smtpd(8) mda_envelope_free() to
 avoid memory leak.
 o Made smtpd(8) use inflateEnd() to tear down the inflate stream in
 uncompress_gzip_chunk().
 o smtpd(8) now stops parsing DNS answers once unpack_rr() reports
 failure.
 o Validate encrypted smtpd(8) queue buffer sizes before processing
 auth tag and IV data.
 o Imported rtrd(8) RPKI-To-Router protocol daemon and rtrctl(8).
 o acme-client(1) saw several changes:
 - Allow wildcards to be specified in alternate names in the
 acme-client(1) config.
 - Made acme-client(1) wipe optarg/eab/eab_key with freezero(3)
 after use.
 - Error check strdup() for external account binding by
 acme-client(1).
 - In acme-client(1), prevent HTTP request injection.
 - Let acme-client(1) handle '=' padding in base64url encoded
 EAB keys.
 - Fixed timegm(3) invocations in acme-client(1).
 - Added support for acme-client(1) external account binding.
 o In bgpd(8):
 - Adjusted bgpd(8) graceful restart timer handling for
 multi-AFI/SAFI sessions.
 - Made bgpd(8) do a prefix re-evaluation if the validation
 state of a route changes.
 - Clear bgpd(8) NEXTHOP_CONNECTED in nexthop_update() if
 msg->connected is false.
 - Made bgpd(8) throttle reads from the peer when
 MSG_PROCESS_LIMIT reached.
 - Fixed bgpd(8) aspa_table_equal() equality comparison.
 - Incorporated new RTR v2 error codes from
 draft-ietf-sidrops-8210bis-26 to bgpd(8).
 - Reworked bgpd(8) IdleHoldTimer and how fast reconnects are
 implemented.
 - Reworked the force_update logic in the bgpd(8) adj-rib-out.
 - Stopped bgpd(8) leaking peer data to bgpctl(8).
 - Implemented ch_meta_locate() in bgpd(8).
 - Brought back the bgpd(8) path_id_tx hack for regular peers.
 - In bgpd(8), improved mrt_dump_entry_mp() calculation
 handling, avoid overflow.
 - Avoid infinite loop when parsing PFKEY replies in iked(8),
 isakmpd(8), bgpd(8), and ldpd(8).
 - Had bgpd(8) make sure the nexthop attribute is present if
 there is any nlri data.
 - Stopped bgpd(8) failing hard on version mismatch; ignore
 extra end-of-params messages.
 - Improved bgpd(8) handling of unknown extended communities.
 - Increased the bgpd(8) MRT attribute buffer to MAX_EXT_PKTSIZE
 so it works in all cases.
 - Fixed use-after-free in bgpd(8) rib_remove and parse.y.
 - Added bgpd(8) force_update flag to force pend_prefix_add()
 calls in adjout_prefix_update().
 - Made bgpd(8) respect RTR min-version in downgrade path and
 properly closing the connection.
 - Improved bgpd(8) add-path send parser. Error out if max is
 used with best.
 - Adjusted handling of limits in bgpd(8) up_generate_addpath().
 - Added extended message capability to checks for what the
 bgpd(8) peer has enabled.
 - Made bgpd(8) return an error on unhandled imsg types in the
 adj-rib-out case.
 - Fixed bgpd(8) port configuring on little endian systems.
 - Extra size checks for bgpd(8) ibuf_set_maxsize().
 - Introduce MAX_ADDPATH_COUNT (set to 100) and use this for the
 bgpd(8) add-path.
 - In bgpd(8) merge_peers() also set local_bgpid for cloned
 peers, not only regular peers.
 - Loop counters converted from uint8_t to u_int in bgpd(8).
 - Reduce maximum configurable stale time to CAPA_GR_TIMEMASK
 (4095) in bgpd(8).
 - In bgpd(8) session_graceful_restart() also arm the
 SessionDown timer.
 - Made bgpd(8) check xp->rdesession to know if the RDE has the
 session running or not.
 - Improved path_calc_hash() in bgpd(8).
 - Fixed 'treat as withdraw' handling for invalid bgpd(8) ORIGIN
 attributes.
 - Fixed two memory accounting issues in bgpd(8) chash.
 - Additional checks on TLV encoding in bgpd(8).
 - Limit all bgpd(8) ASPATH attributes to 750 elements.
 - In bgpd(8), prevent overflow of the uint8_t length value in
 attr_optadd.
 - Re-evaluate bgpd(8) prefixes if just PREFIX_FLAG_FILTERED
 changed.
 o In rpki-client(8):
 - Fixed rpki-client(8) to avoid buffer overreads with OpenSSL
 4.1.
 - In rpki-client(8), reject non-conformant certificate subject
 encodings.
 - Made rpki-client(8) check alignment of certificate CRLDPs
 with the referring Manifest.
 - Reworked rpki-client(8) cms_parse_validate().
 - Fixed handling of inherited resources in leaves by
 rpki-client(8).
 - Unified all signed object parser functions in rpki-client(8).
 - rpki-client(8) now unconditionally warns about incorrect RSA
 parameters; rejects some malformed ROAs.
 - Limit the range of deltas added to the rpki-client(8) queue.
 - Ensure consistent states in persistent rpki-client(8) HTTP
 connections.
 - Removed behaviour difference between rpki-client(8) versions
 with and without gbr support.
 - Fixed possible exit race in the rpki-client(8) parser.
 - Made rpki-client(8) only record NCA history on successful
 runs.
 - rpki-client(8) will now only output config files on
 successful run.
 - Batch rpki-client(8) retries of non-functional CAs based on
 their rsync base URI.
 - Properly apply constraints to rpki-client(8) BGPsec Router
 certs.
 - Deduplicated rpki-client(8) skiplist, shortlist, and NCA
 retry handling.
 - Removed incorrect free in rpki-client(8) nca_hist_load().
 - In rpki-client(8) cert_ca_sia(), use the correct notify
 string in error message.
 - Removed double fclose in a success path in rpki-client(8).
 - Added a coinflip to increase cycle-to-cycle jitter in
 rpki-client(8).
 - In rpki-client(8), added a backoff retry mechanism for
 non-functional CAs.
 - rpki-client(8) now rejects certs with duplicate extension
 OIDs.
 - Clear last_modified after each response on a persistent HTTP
 rpki-client(8) connection.
 - In rpki-client(8), switch subordinates in CCR manifests to a
 simple queue.
 - Made rpki-client(8) exclude hidden files and directories when
 synchronising via rsync.
 - In rpki-client(8), limited the length of filenames in some
 ASN.1 fields to 255.
 - Fixed incomplete strncmp() check in rpki-client(8).
 - Fix off-by-one in rpki-client(8) ip_addr_check_overlap().
 - Fixed shortlist and skiplist checks in rpki-client(8).
 - Added more error checks and safeguards to rpki-client(8).

 - tmux(1) improvements and bug fixes:
 o Keep the scroll position in tree mode when the list is rebuilt
 (issue 5631).
 o Do not leak waiting clients (in wait-for) if they are killed
 (issue 5614).
 o Do not cancel mark when a click is on the border.
 o Added support for borderless menus, like panes.
 o Added utf8 terminal-features.
 o Ignore focus events earlier to avoid them interfering with prefix.
 o Added -K flag to new-pane to make a modal pane capture all keys.
 o Always unzoom before splitting windows, including for floating
 panes.
 o Added 'T' to change pane title.
 o Added refresh-now command.
 o Ignore Ms if it is invalid (eg no %p1), report in client mode.
 o Fixed crash when synchronising groups and there is no current
 window.
 o Added pane_private_modes format with list of DEC private modes.
 o Prevented core dumps upon startup on landisk.
 o Added modal panes, created currently with new-pane -O.
 o Major rework of prompts.
 o Fixed cursor calculation when the status line is at the top.
 o Added -H flag to capture-pane to show hyperlinks.
 o Added -L to show line numbers with capture-pane and -F to show
 line flags.
 o Clear entire lines when removing from history or freeing.
 o Redraw entire session when making a new pane.
 o Added -g flag to kill-session to kill all sessions in a group.
 o Fixed crash when freeing layout cell.
 o Added missing argument to %unlinked-window-renamed.
 o Increase escape delay if the buffer contains a partial paste end.
 o Fixed crash caused by including unattached clients on sorted list.
 o Added new-pane command.
 o Fixed infinite loop due to underflow when redrawing scrollbar.
 o Fixed control mode teardown ordering for queued pane output.
 o Added Emacs-style re-centre-top-bottom.
 o Added time limits to some loops.
 o Added missing flags to screen_mode_to_string.

 - LibreSSL version 4.4.0:
 o Portable changes:
 - Numerous compatibility layer fixes for AIX, FreeBSD, macOS,
 MinGW, NetBSD, and especially Windows.
 - Fixed incorrect code generation by the MSVC ARM64 optimizer
 in constant-time bignum code.
 - Improved assembly support on many platforms.
 - Fixed openssl(1), nc(1), and ocspcheck(8) silently running
 without pledge(2) and unveil(2) on hosts that provide them.
 o Internal improvements:
 - Minor code cleanup for PKCS#7.
 - Clear unused bits for the maximum of RFC 3779 IP address
 ranges.
 - Cleanup passes over the DTLS code, avoiding many contortions.
 - Zero out the failure_key in ML-KEM code.
 - Improve portability in preprocessor based SHA assembly.
 - Removed a few vestigial #ifdefs from public and internal
 headers.
 - Introduce and use dtls12_handshake_msg framework.
 - Rename union from _ to u in the ui code. Avoids Windows CE
 #ifdef.
 - Clean up and simplify signature algorithm handling after
 removal of TLSv1.0 and TLSv1.1.
 - Add a point at infinity check to ecdh_compute_key().
 - Fix incorrect purpose check in unreachable non-legacy path of
 the modern X.509 verifier.
 - Improve TLSv1.3 server handling of no shared groups.
 - Correct secondary key share handling for HelloRetryRequests.
 - Fix EXFLAG_CRITICAL mishandling in the crl_cb().
 - Among CRLs with the same score prefer the one with the most
 recent thisUpdate to match BoringSSL and OpenSSL behavior.
 - Clean up sequence number and message header handling in DTLS.
 - Remove redundant BIO_write() length assertions in
 b64_write().
 - Report invalid base64 BIO state as an internal error rather
 than asserting.
 - Improve SHA-3 performance by using an unrolled and
 interleaved algorithm.
 - Allocate TLSv1.3 receive buffers lazily.
 - Simplify handling of remaining record content on switch to
 the legacy stack.
 - Avoid harmless narrowing of the return value in dtls1_ctrl().
 - Remove NID_md5_sha1 support from tls1_PRF().
 - Remove DTLS unprocessed records queue.
 - Remove DTLS application data queue.
 - Remove SSL3_FLAGS_NO_RENEGOTIATE_CIPHERS which was never set.
 o Compatibility changes:
 - The misnamed tls_peer_cert_chain_pem() has been deprecated
 and may be removed in a future release.
 tls_peer_cert_chain_verified_pem() and
 tls_peer_cert_bundle_unverified_pem() should be used instead.
 - Use X25519MLKEM768 as the preferred group for TLSv1.3
 connections in libtls.
 - Ensure libtls keeps working with future OpenSSL releases that
 will stop NUL-terminating ASN.1 strings. This is an old bug
 in libtls that will bite, probably starting with OpenSSL 4.2.
 - CRYPTO_cleanup_all_ex_data() is now a no-op. It was not
 thread safe and the actual cleanup is now done by
 OPENSSL_cleanup(3).
 - Align X509_check_ca(3) with modern OpenSSL. While it has long
 been documented that it only works after calling
 X509_check_purpose(3), it still makes sense to "fail closed",
 i.e., indicate a non-CA.
 - Added OIDs for CCR, ErikIndex, ErikPartition,
 ErikSegmentIndex, and communityDefinition.
 o Bug fixes:
 - Fix PKCS7_set_{un,}signed_attributes(3) to allow caller to
 free on failure rather than risking a double free.
 - Initialize decode_error and invalid_key variables in TLS key
 share code to avoid branching on uninitialized memory.
 - Record extension length between type and data in the
 ClientHello hash to ensure identical framing in first and
 second CH.
 - Fix out of bound writes in the s_client XMSS mode.
 - Ensure EC_GROUP_check(3) and X509_CRL_verify(3) failures
 result in "app" failures in openssl(1) ecparam and openssl
 crl.
 - Do not fail accept on reverse DNS lookup failures in
 s_socket.
 - Ensure X509V3_EXT_print(3) only returns 0 and 1.
 - Avoid calling memcmp() on NULL in IPAddressFamily_cmp().
 - In libtls disallow wildcard matching of a TLD specified as a
 FQDN.
 - Unbreak some aspects of TLSv1.2 with custom curve lists.
 - Ensure a peer-provided EC public key uses uncompressed
 encoding.
 - Send decode_error alert on failure to decode an EC peer
 pubkey.
 - Avoid NULL dereference and out-of-bounds read in
 password-based CMS decryption.
 - Add some missing bounds check to ASN1_mbstrinc_copy().
 - Avoid freeing a caller-owned buffer in PKCS7_verify(3).
 - Remove SSL_OP_LEGACY_SERVER_CONNECT from default options.
 - Send illegal parameter alerts for various HelloRetryRequest
 violations.
 - Check that the server selected ciphersuite is valid for use
 with TLSv1.2.
 - Unlock CRYPTO_LOCK_UI on ui_open_session() failure to avoid a
 deadlock.
 - Check HMAC(3) return value to avoid later use of
 uninitialized in openssl(1).
 - Use correct alert for key_share without supported_groups.
 - Don't drop X509_V_ERR_HOSTNAME_MISMATCH when verify callback
 returns 1. It has long been documented that this is ill
 advised but some applications still do it.
 - Ensure the server selects an ALPN protocol that we advertised
 or abort the handshake with illegal_parameter.
 - Fix streaming of PKCS#7 objects with omitted content.
 - Avoid OOB access due to type confusion in PKCS7_stream().
 - Plug leak and various other bugs in asn1_multi(), a helper to
 handle sequences and sets in config parsing.
 - Fix RFC 3779 inheritance checks for leaves as far as possible
 without breaking the RPKI. Still allow the immediate issuer
 to omit one of the extensions because otherwise about one
 third of RFC 9286 Manifests would become invalid.
 - Correct a botched size check in dtls1_process_fragment().
 - Avoid confusing delta CRLs as full CRLs.
 - When copying an RSA-PSS EVP_PKEY_CTX, ensure saltlen and
 minimal saltlen restrictions are copied rather than using the
 defaults.
 - Allow DTLS clients to receive unexpected Finished messages.
 - Cache the leaf's extensions before adding it to a validated
 chain to make name constraints check work more reliably.
 - Ensure the whole subject is searched for email addresses and
 common names.
 - Check for embedded NULs in emails and subjectAltname in the
 essentially unused legacy NAME_CONSTRAINTS_*() API.
 - Remove support for nameRelativeToCRLIssuer in the CRL
 Distribution Point extension. Per RFC 5280 it SHOULD not be
 used by conforming CAs and it was eating memory for breakfast
 pre-signature.
 o Security and reliability fixes:
 - Fix parsing issues in X.509 name constraints URI host
 parsing. Handle IPv6 literals correctly and don't allow
 specially crafted userinfo to bypass host checks.
 - Limit size of buffered DTLS handshake messages to avoid
 overly large memory consumption on small handshake message
 fragments.
 - Fix an OCSP responder authorization bypass for clients using
 tls_config_ocsp_require_stapling(), of which only OpenBSD
 nc(1) and ftp(1) are known when they're used with the
 "muststaple" key word.
 o Testing and proactive security:
 - Improved test coverage for DTLS and TLS renegotiation.
 - Add X.509 CRL regress from pre-Apache2-licensed BoringSSL.
 - Rework the testing framework to be memory based rather than
 file based. Match Go's output format more closely.

 - OpenSSH 10.6:
 o Security fixes:
 - Disabled ssh(1) LZ77 dictionary coder to avoid a potential
 side-channel leak.
 - Fixed ChannelTimeout and RekeyLimit not being applied in
 sshd_config(5).
 - Made ssh(1) authorized_keys "restrict" keyword apply
 correctly to tunnel forwarding.
 o Potentially incompatible changes:
 - Use IANA allocated codepoint for ssh-mldsa44-ed25519 instead
 of '@openssh.com'.
 - Made sshd_config(5) DisableForwarding=yes override
 PermitTunnel=yes.
 - Enforce a maximum size for usernames in ssh-agent(1) agent
 key use constraints.
 - Disallow NUL byte in scp(1) '-O filename'.
 o New features:
 - New ssh-add(1) option '-P' to skip PIN entry (bz3635).
 - ssh(1) signal handling with readpassphrase(3) fixed.
 - Switched ssh(1) from supercop ed25519 to libsodium.
 - Extended ssh(1) TCPKeepAlive to support forwardings (bz3921).
 - Added ssh-keygen(1) 'hexdump' to dump the key blob in hex
 format.
 - Allow setting/clearing ssh-keygen(1)
 touch-required/verify-required flags on FIDO private keys
 when resetting the passphrase.
 - Added ssh(1) '-Z user@host' mode that lists pubkeys that will
 be tried for authentication.
 - Added experimental ssh(1) support for composite post-quantum
 mldsa44-ed25519 signature scheme.
 - Added an explicit-seed variant of the ssh(1) keygen function.
 - Added signature malleability and pubkey validity checks to
 sshd(8) ed25519 verification.
 o Bugfixes:
 - Check ssh(1) compressed payloads don't inflate beyond the
 maximum payload length.
 - Avoid race between multiple ssh(1) processes establishing
 multiplexing control socket.
 - Plugged memory leak in ssh-add(1) (CID 913600).
 - Fix for ssh(1) CIDs 913601 and 913602.
 - Fix for ssh(1) CID 913600.
 - Converted ssh(1) channel timeouts to allow fractional and
 subsecond timeouts.
 - Made ssh(1) masking signals correctly use sigaddset (bz3981).
 - Fixed ssh(1) memleaks (CID 913598 and 913599); added missing
 semicolon (CID 913599).
 - Corrected Daylight Savings Time timestamp conversion by
 ssh(1) (bz4004).
 - Fixed ssh(1) proxy socket breakage in t-multiplex after
 recent pledge(2) changes.
 - Reading server banner by ssh-keyscan(1) no longer
 blocks/freezes on a many-host keyscan.
 - Allow session-bind@openssh.com requests when the ssh(1) agent
 is locked.
 - Avoid potential realloc use-after-free in the ssh(1) client.
 - Reordering of certificates tried during ssh(1) pubkey
 authentication.
 - Fixed ssh(1) ML-KEM/ECDH interop problem.
 - Removed some key ssh(1) parsing and verification paths from
 the pre-auth attack surface.
 - Avoid download to server-controlled path when performing
 ssh(1) download via commandline.
 - Avoid possible NULL deref in ssh(1); sanitise filenames
 received via remote glob.
 - Large refactoring of sshd(8) config management code.
 - Made sshd(8) force domain name received from the system
 resolver to lowercase.
 - Fixed two one-byte out-of-cound reads in sshd(8).
 - Stricter validation of transport state passed from the
 preauth to postauth sshd(8) process.
 - Fixed ssh(1) client use-after-free on error path if
 cipher_init() fails.
 - Added ssh-agent(1) -V to print version, use it to test the
 binary is functional after relinking.
 - Stopped ssh(1) validating bad cipher/mac lists arguments as
 valid.
 - Fixed ssh(1) NULL deref during pubkey auth.
 - Dropbear recently added a -Q option; make ssh(1) use it to
 query KEX if available.
 - Classify ssh(1) dynamic-tcpip channels as bulk, not
 interactive (bz3958).

 - Ports and packages:
 o Pre-built packages are available for the following architectures on
 the day of release:
 - aarch64 (arm64): 12907
 - amd64: 13060
 - i386: 10659
 - mips64: 9072
 - powerpc64: 9564
 - sparc64: 10621
 o Packages for the following architectures will be made available as
 their builds complete:
 - arm
 - powerpc
 - riscv64

 - Some highlights:

 o Asterisk 20.21.0 and 22.11.0 o OCaml 4.14.2
 o Audacity 3.7.9 o OpenLDAP 2.6.15
 o CMake 4.3.5 o PHP 8.3.33, 8.4.26 and
 o Chromium 154.0.8037.92 8.5.11
 o Emacs 31.1 o Postfix 3.5.28 and 3.11.7
 o FFmpeg 9.0.2 o PostgreSQL 18.6
 o GCC 16.1.0 o Prism Launcher 11.1.0
 o GHC 9.10.3 o Python 2.7.18 and 3.14.7
 o GNOME 49 o Qt 5.15.19 (+ kde patches) and
 o Go 1.27.1 6.11.2
 o JDK 11.0.32, 17.0.20, 21.0.12, o R 4.6.1
 and 25.0.4 o Ruby 3.3.12, 3.4.11 and 4.0.7
 o KDE Gear 26.08.1 o Rust 1.98.1
 o KDE Frameworks 6.30.0 o SQLite 3.53.2
 o KDE Plasma 6.7.5 o Shotcut 26.8.1
 o Krita 6.0.3 o Sudo 1.9.17p2
 o LLVM/Clang 21.1.8 and 22.1.8 o Suricata 7.0.7
 o LibreOffice 26.8.0.3 o Tcl/Tk 8.5.19, 8.6.18 and 9.0.4
 o Lua 5.1.5, 5.2.4, 5.3.6, o TeX Live 2026
 5.4.8 and 5.5.1 o Vim 9.2.1125, Neovim 0.12.5 and
 o MariaDB 12.3.3 Vim-Classic 2026091
 o Mono 6.14.1 o Wayland 1.26.0 with compositors
 o Mozilla Firefox 157.0 and CoW, Labwc, Mango, Niri, Sway and
 ESR 153.4.0 Wayfire
 o Mozilla Thunderbird 153.4.0 o Vulkan 1.4.357.0
 o Mutt 2.4.2 and NeoMutt 20260616 o Xfce 4.20.0
 o Node.js 24.21.0 and Deno 2.9.7

 - As usual, steady improvements in manual pages and other documentation.

 - The system includes the following major components from outside suppliers:
 o Xenocara (based on X.Org 7.7 with xserver 21.1.24 + patches,
 freetype 2.14.3, fontconfig 2.17.1, Mesa 25.0.7, xterm 410,
 xkeyboard-config 2.20, fonttosfnt 1.2.5 and more)
 o LLVM/Clang 22.1.6 (+ patches)
 o GCC 4.2.1 (+ patches) and 3.3.6 (+ patches)
 o Perl 5.42.3 (+ patches)
 o pkgconf 3.0.7
 o NSD 4.15.2
 o Unbound 1.26.1
 o Ncurses 6.4
 o Binutils 2.17 (+ patches)
 o GDB 6.3 (+ patches)
 o Awk 20250116
 o Expat 2.8.4
 o zlib 1.3.2 (+ patches)

------------------------------------------------------------------------
- SECURITY AND ERRATA --------------------------------------------------

We provide patches for known security threats and other important
issues discovered after each release. Our continued research into
security means we will find new security problems -- and we always
provide patches as soon as possible. Therefore, we advise regular
visits to

 https://www.OpenBSD.org/security.html
and
 https://www.OpenBSD.org/errata.html

------------------------------------------------------------------------
- MAILING LISTS AND FAQ ------------------------------------------------

Mailing lists are an important means of communication among users and
developers of OpenBSD. For information on OpenBSD mailing lists, please
see:

 https://www.OpenBSD.org/mail.html

You are also encouraged to read the Frequently Asked Questions (FAQ) at:

 https://www.OpenBSD.org/faq/

------------------------------------------------------------------------
- DONATIONS ------------------------------------------------------------

The OpenBSD Project is a volunteer-driven software group funded by
donations. Besides OpenBSD itself, we also develop important software
like OpenSSH, LibreSSL, OpenNTPD, OpenSMTPD, the ubiquitous pf packet
filter, the quality work of our ports development process, and many
others. This ecosystem is all handled under the same funding umbrella.

We hope our quality software will result in contributions that maintain
our build/development infrastructure, pay our electrical/internet costs,
and allow us to continue operating very productive developer hackathon
events.

All of our developers strongly urge you to donate and support our future
efforts. Donations to the project are highly appreciated, and are
described in more detail at:

 https://www.OpenBSD.org/donations.html

------------------------------------------------------------------------
- OPENBSD FOUNDATION ---------------------------------------------------

For those unable to make their contributions as straightforward gifts,
the OpenBSD Foundation (https://www.openbsdfoundation.org) is a Canadian
not-for-profit corporation that can accept larger contributions and
issue receipts. In some situations, their receipt may qualify as a
business expense write-off, so this is certainly a consideration for
some organizations or businesses.

There may also be exposure benefits since the Foundation may be
interested in participating in press releases. In turn, the Foundation
then uses these contributions to assist OpenBSD's infrastructure needs.
Contact the foundation directors at directors@openbsdfoundation.org for
more information.

------------------------------------------------------------------------
- RELEASE SONG ---------------------------------------------------------

OpenBSD 8.0 comes with the song "The Simps on AI". An explanation
of the song may be found at:

 https://www.OpenBSD.org/lyrics.html#80

------------------------------------------------------------------------
- HTTPS INSTALLS -------------------------------------------------------

OpenBSD can be easily installed via HTTPS downloads. Typically you need
a single small piece of boot media (e.g., a USB flash drive) and then
the rest of the files can be installed from a number of locations,
including directly off the Internet. Follow this simple set of
instructions to ensure that you find all of the documentation you will
need while performing an install via HTTPS.

1) Read either of the following two files for a list of HTTPS mirrors
 which provide OpenBSD, then choose one near you:

 https://www.OpenBSD.org/ftp.html
 https://ftp.openbsd.org/pub/OpenBSD/ftplist

 As of October 20, 2026, the following HTTPS mirror sites have the
 8.0 release:

 https://cdn.openbsd.org/pub/OpenBSD/8.0/ Global
 https://ftp.eu.openbsd.org/pub/OpenBSD/8.0/ Stockholm, Sweden
 https://ftp.hostserver.de/pub/OpenBSD/8.0/ Frankfurt, Germany
 https://ftp.bytemine.net/pub/OpenBSD/8.0/ Oldenburg, Germany
 https://ftp.fr.openbsd.org/pub/OpenBSD/8.0/ Paris, France
 https://mirror.aarnet.edu.au/pub/OpenBSD/8.0/ Brisbane, Australia
 https://ftp.usa.openbsd.org/pub/OpenBSD/8.0/ CO, USA
 https://ftp5.usa.openbsd.org/pub/OpenBSD/8.0/ CA, USA
 https://mirror.esc7.net/pub/OpenBSD/8.0/ TX, USA
 https://openbsd.cs.toronto.edu/pub/OpenBSD/8.0/ Toronto, Canada
 https://cloudflare.cdn.openbsd.org/pub/OpenBSD/8.0/ Global
 https://fastly.cdn.openbsd.org/pub/OpenBSD/8.0/ Global

 The release is also available at the master site:

 https://ftp.openbsd.org/pub/OpenBSD/8.0/ Alberta, Canada

 However it is strongly suggested you use a mirror.

 Other mirror sites may take a day or two to update.

2) Connect to that HTTPS mirror site and go into the directory
 pub/OpenBSD/8.0/ which contains these files and directories.
 This is a list of what you will see:

 ANNOUNCEMENT armv7/ octeon/ root.mail
 README hppa/ openbsd-80-base.pub sparc64/
 SHA256 i386/ packages/ src.tar.gz
 SHA256.sig landisk/ packages-stable/ sys.tar.gz
 alpha/ loongson/ ports.tar.gz xenocara.tar.gz
 amd64/ luna88k/ powerpc64/
 arm64/ macppc/ riscv64/

 It is quite likely that you will want at LEAST the following
 files which apply to all the architectures OpenBSD supports.

 README - generic README
 root.mail - a copy of root's mail at initial login.
 (This is really worthwhile reading).

3) Read the README file. It is short, and a quick read will make
 sure you understand what else you need to fetch.

4) Next, go into the directory that applies to your architecture,
 for example, amd64. This is a list of what you will see:

 BOOTIA32.EFI* bsd* floppy80.img pxeboot*
 BOOTX64.EFI* bsd.mp* game80.tgz xbase80.tgz
 BUILDINFO bsd.rd* index.txt xfont80.tgz
 INSTALL.amd64 cd80.iso install80.img xserv80.tgz
 SHA256 cdboot* install80.iso xshare80.tgz
 SHA256.sig cdbr* man80.tgz
 base80.tgz comp80.tgz miniroot80.img

 If you are new to OpenBSD, fetch _at least_ the file INSTALL.amd64
 and install80.iso. The install80.iso file (roughly 794MB in size)
 is a one-step ISO-format install CD image which contains the various
 *.tgz files so you do not need to fetch them separately.

 If you prefer to use a USB flash drive, fetch install80.img and
 follow the instructions in INSTALL.amd64.

5) If you are an expert, follow the instructions in the file called
 README; otherwise, use the more complete instructions in the
 file called INSTALL.amd64. INSTALL.amd64 may tell you that you
 need to fetch other files.

6) Just in case, take a peek at:

 https://www.OpenBSD.org/errata.html

 This is the page where we talk about the mistakes we made while
 creating the 8.0 release, or the significant bugs we fixed
 post-release which we think our users should have fixes for.
 Patches and workarounds are clearly described there.

------------------------------------------------------------------------
- X.ORG FOR MOST ARCHITECTURES -----------------------------------------

X.Org has been integrated more closely into the system. This release
contains X.Org 7.7. Most of our architectures ship with X.Org, including
amd64, sparc64 and macppc. During installation, you can install X.Org
quite easily using xenodm(1), our simplified X11 display manager forked
from xdm(1).

------------------------------------------------------------------------
- PACKAGES AND PORTS ---------------------------------------------------

Many third party software applications have been ported to OpenBSD and
can be installed as pre-compiled binary packages on the various OpenBSD
architectures. Please see https://www.openbsd.org/faq/faq15.html for
more information on working with packages and ports.

Note: a few popular ports, e.g., NSD, Unbound, and several X
applications, come standard with OpenBSD and do not need to be installed
separately.

------------------------------------------------------------------------
- SYSTEM SOURCE CODE ---------------------------------------------------

The source code for all four subsystems can be found in the
pub/OpenBSD/8.0/ directory:

 xenocara.tar.gz ports.tar.gz src.tar.gz sys.tar.gz

The README (https://ftp.OpenBSD.org/pub/OpenBSD/8.0/README) file
explains how to deal with these source files.

------------------------------------------------------------------------
- THANKS ---------------------------------------------------------------

Ports tree and package building by Jeremie Courreges-Anglas,
Visa Hankala, Stuart Henderson, Peter Hessler, George Koehler,
Kurt Mosiejczuk, and Christian Weisgerber. Base and X system builds by
Kenji Aoyama and Theo de Raadt. Release art by
"yvaneht nioj and clanker".

We would like to thank all of the people who sent in bug reports, bug
fixes, donation cheques, and hardware that we use. We would also like
to thank those who bought our previous CD sets. Those who did not
support us financially have still helped us with our goal of improving
the quality of the software.

Our developers are:

 Aaron Bieber, Adam Wolk, Aisha Tammy, Alexander Bluhm,
 Alexander Hall, Alexandr Nedvedicky, Alexandr Shadchin,
 Alexandre Ratchov, Andrew Hewus Fresh, Anil Madhavapeddy,
 Anthony J. Bentley, Antoine Jacoutot, Anton Lindqvist, Asou Masato,
 Ayaka Koshibe, Benoit Lecocq, Bjorn Ketelaars, Bob Beck,
 Brandon Mercer, Brent Cook, Bryan Steele, Can Erkin Acar,
 Caspar Schutijser, Charlene Wendling, Charles Longeau,
 Chris Cappuccio, Christian Ludwig, Christian Weisgerber,
 Christopher Zimmermann, Claudio Jeker, Dale Rahn, Damien Miller,
 Daniel Dickman, Daniel Jakots, Darren Tucker, Dave Voutila,
 David Coppa, David Gwynne, David Hill, David Leadbeater,
 Denis Fondras, Edd Barrett, Eric Faurot, Florian Obser,
 Florian Riehm, Frederic Cambus, George Koehler, Gerhard Roth,
 Giannis Tsaraias, Gilles Chehade, Giovanni Bechis, Gleydson Soares,
 Gonzalo L. Rodriguez, Greg Steuck, Hans-Joerg Hoexer, Helg Bredow,
 Henning Brauer, Ian Darwin, Igor Sobrado, Ingo Feinerer,
 Ingo Schwarze, James Hastings, James Turner, Jan Klemkow,
 Jason McIntyre, Jasper Lievisse Adriaanse, Jeremie Courreges-Anglas,
 Jeremy Evans, Job Snijders, Joel Sing, Joerg Jung,
 Johannes Thyssen Tishman, Jonathan Armani, Jonathan Gray,
 Jonathan Matthew, Jordan Hargrave, Josh Rickmar, Joshua Sing,
 Joshua Stein, Juan Francisco Cantero Hurtado, Kazuya Goda,
 Kenji Aoyama, Kenjiro Nakayama, Kenneth R Westerback,
 Kent R. Spillner, Kevin Lo, Kirill A. Korinsky, Kirill Bychkov,
 Klemens Nanni, Kurt Miller, Kurt Mosiejczuk, Landry Breuil,
 Lawrence Teo, Lucas Gabriel Vuotto, Lucas Raab, Marcus Glocker,
 Mark Kettenis, Mark Lumsden, Markus Friedl, Martijn van Duren,
 Martin Natano, Martin Reindl, Martynas Venckus, Matthew Dempsky,
 Matthias Kilian, Matthieu Herrb, Michael Mikonos, Mike Belopuhov,
 Mike Larkin, Miod Vallat, Moritz Buhl, Nam Nguyen,
 Nayden Markatchev, Nicholas Marriott, Nigel Taylor, Okan Demirmen,
 Omar Polo, Ori Bernstein, Otto Moerbeek, Paco Esteban,
 Pamela Mosiejczuk, Pascal Stumpf, Patrick Wildt, Paul Irofti,
 Pavel Korovin, Peter Hessler, Philip Guenther,
 Pierre-Emmanuel Andre, Pratik Vyas, Rafael Sadowski,
 Rafael Zalamena, Ralph Covelli, Raphael Graf, Remi Locherer,
 Remi Pointel, Renato Westphal, Renaud Allard, Ricardo Mestre,
 Richard Procter, Rob Pierce, Robert Nagy, Sasano Takayoshi,
 Scott Soule Cheloha, Sebastian Benoit, Sebastian Reitenbach,
 Sebastien Marie, Solene Rapenne, Stefan Fritsch, Stefan Hagen,
 Stefan Kempf, Stefan Sperling, Steven Mestdagh, Stuart Cassoff,
 Stuart Henderson, Sunil Nimmagadda, T.J. Townsend, Ted Unangst,
 Theo Buehler, Theo de Raadt, Thomas Frohwein, Tim van der Molen,
 Tobias Heider, Tobias Stoeckmann, Todd C. Miller, Todd Mortimer,
 Tom Cosgrove, Tracey Emery, Ulf Brosziewski, Uwe Stuehler,
 Vadim Zhukov, Vincent Gross, Visa Hankala, Vitaliy Makkoveev,
 Volker Schlecht, Yasuoka Masahiko, Yojiro Uo

[prev in list] [next in list] [prev in thread] [next in thread]
댓글 (0)
로그인하면 이 기사에 내 생각을 남길 수 있어요